01 · BASELINE
Baseline Technical Security Assessment
Establish the normal physical and electronic environment, inspect agreed sensitive areas and document findings, vulnerabilities and practical recommendations.
Protect confidential conversations before there is a problem. We provide routine and event-driven corporate TSCM for organisations handling commercially sensitive information — whether or not there is any specific suspicion that surveillance is present.
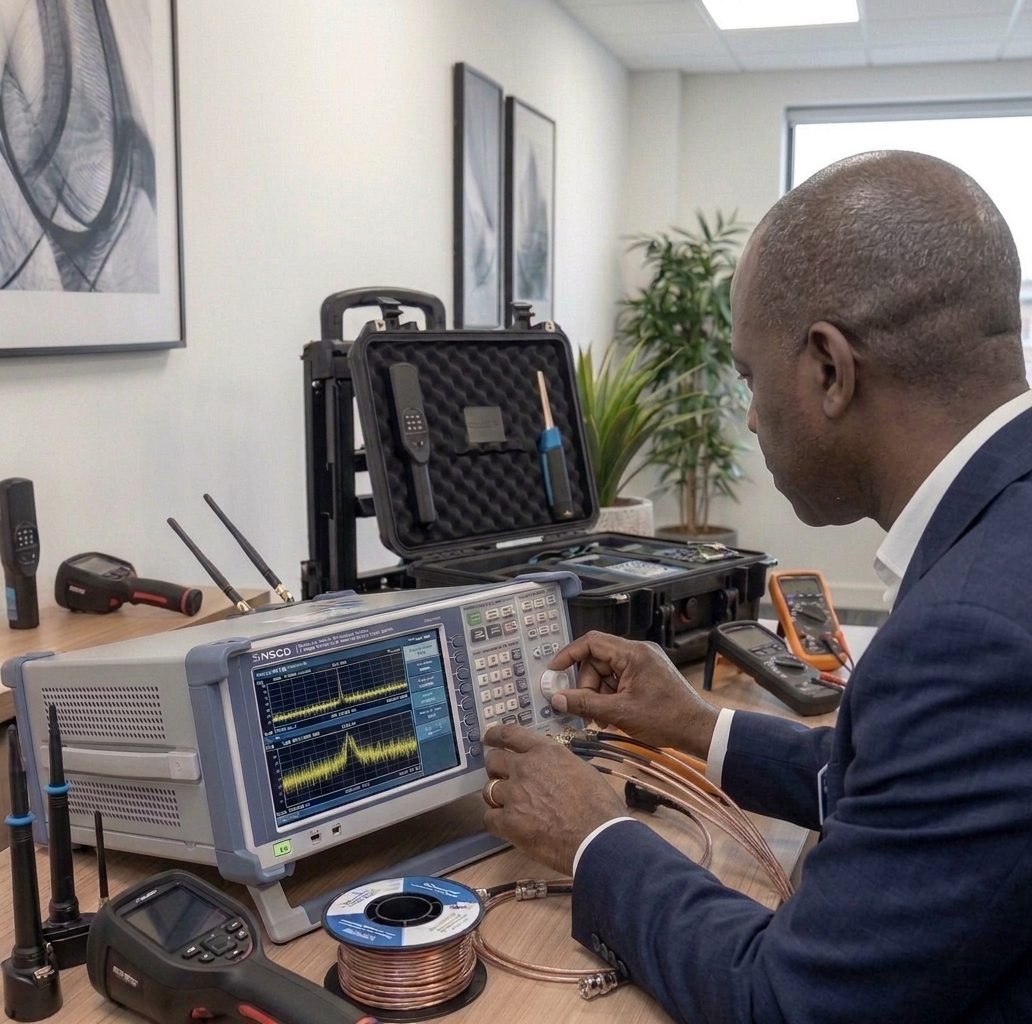
Your organisation already protects its networks, devices and premises. Corporate TSCM extends that security thinking to confidential conversations and sensitive physical environments. A company does not need to suspect an active bug before there is a valid reason to protect a boardroom, executive office or meeting area.
Establish the normal physical and electronic environment, inspect agreed sensitive areas and document findings, vulnerabilities and practical recommendations.
Scheduled inspections can provide ongoing assurance for organisations that regularly handle commercially sensitive information. Routine programmes can be tailored to the organisation's risk profile rather than requiring a fixed inspection schedule.
Targeted inspection before acquisitions, major tenders, litigation meetings, investment negotiations, product launches or other high-value confidential discussions.
A technical-security review can also be appropriate after construction, refurbishment, cabling work or other periods when contractors have had unusual access to sensitive areas. The scope is agreed around the actual changes and access history.
K9 Electronics can support deeper technical work through its in-house RF laboratory, electronics workshop and precision manufacturing capability. This is particularly useful when a client wants a repeatable technical baseline or verification after changes to a sensitive environment.
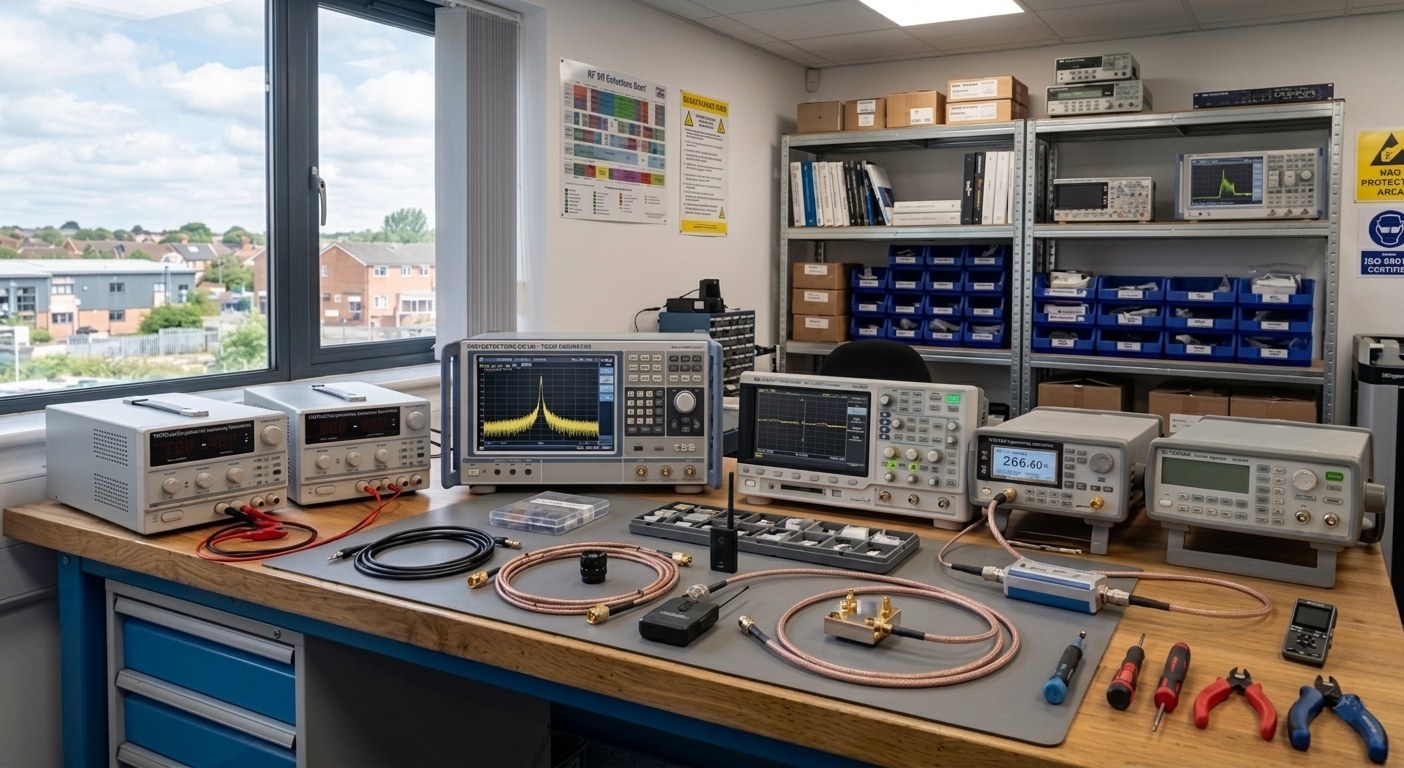
Preventative corporate TSCM is designed for organisations with information worth protecting, not only organisations that already believe surveillance is present. The service can be aligned to business risk, sensitive events, unusual access and the areas where confidential decisions are made.
Boardrooms, strategy rooms and executive areas where confidential commercial decisions are discussed.
Before or during acquisitions, negotiations, financing discussions and other commercially sensitive transactions.
Meeting rooms used for privileged discussions, disputes, investigations or confidential client matters.
Environments where product development, intellectual property or confidential engineering information is discussed.
After construction, cabling, maintenance or other periods when third parties have had unusual access to sensitive rooms or infrastructure.
Scheduled technical-security inspections for organisations that want ongoing assurance around boardrooms, executive offices and other sensitive areas.
Companies routinely review cyber security, access control and physical security. Sensitive conversations and meeting environments can also benefit from periodic technical-security assessment. Corporate TSCM does not need to begin with a suspicion that a listening device is present.
Six- or twelve-monthly inspections can help organisations that regularly handle commercially sensitive information maintain an independent technical-security check of key rooms.
Refurbishment, cabling work, contractor access, fit-out changes or significant personnel changes can justify a targeted review of sensitive areas and their normal electronic environment.
Additional TSCM can be scheduled before major board meetings, transactions, tenders, legal discussions, negotiations and other high-value confidential events.
A room can be free of surveillance devices and still allow sensitive information to escape. For boardrooms, executive offices and meeting rooms, we can carry out a practical screening assessment of obvious acoustic and RF privacy leakage before important conversations take place.
Controlled speech or test audio is used to assess whether conversation can be heard or understood at relevant positions outside the intended private area, helping identify obvious weak points such as doors, glazing, partitions and adjoining spaces.
Indicative measurements compare radio-frequency signal levels inside and outside the room to assess how effectively the space attenuates wireless/RF energy and to highlight obvious leakage paths.
We document the areas checked, observations, indicative measurements, identified weak points and practical recommendations, including when more specialised testing may be appropriate.
This service is intended as a practical meeting-room privacy assessment. It is not presented as certified acoustic testing, TEMPEST testing or formal EMC/shielding-effectiveness certification.
For acquisitions, major tenders, legal discussions, investment negotiations, product launches or other commercially important conversations, a sensitive-event TSCM inspection can be carried out shortly before the meeting. It can also be combined with a privacy-leakage assessment where acoustic or RF exposure is part of the requirement.
For organisations with recurring confidentiality requirements, we can provide scheduled inspections and event-driven TSCM support rather than treating every attendance as an isolated bug sweep. The programme is tailored to the organisation, the rooms that matter and how often the risk changes.
Establish the agreed rooms, normal RF environment, relevant equipment, access history and practical vulnerabilities.
Periodic technical-security reviews at an interval appropriate to the organisation and risk profile.
Additional TSCM before transactions, negotiations, board meetings or other high-value confidential events.
A known technical provider can respond more efficiently when a suspicious item, unusual signal or access concern is later identified.
Review findings, changes to rooms and equipment, recurring anomalies and whether the inspection scope or frequency should change.
Maintain a practical record of agreed scope, inspections, significant findings and recommended follow-up for internal security management.
An organisation may only need a baseline assessment plus annual review, while another may benefit from six-monthly inspections and additional event-triggered work. We quote according to the rooms, frequency, reporting and response requirements rather than forcing every client into the same package.
The first inspection establishes the agreed technical-security scope and helps build an understanding of the normal physical and electronic environment. Findings are assessed in context rather than assuming every unusual signal is surveillance, and subsequent visits can focus more quickly on meaningful changes and anomalies.
We establish the areas of concern, access history, sensitive rooms and any specific events that may affect the survey.
The radio environment is assessed using professional test equipment, with suspicious or unexplained signals investigated further.
Appropriate physical examination is combined with electronic detection methods rather than relying on a single handheld detector.
We explain what was examined, significant findings, vulnerabilities, limitations and practical next steps, including whether routine or event-triggered follow-up is appropriate.
Modern corporate environments contain Wi-Fi, Bluetooth, mobile devices, wireless presentation systems, access control, IoT equipment and other legitimate RF sources. Simply detecting radio energy is not enough.
Small defined meeting-room inspections may start from £795. Broader corporate assessments, routine assurance programmes and sensitive-event requirements are quoted according to scope and frequency.
The appropriate scope depends on the premises and threat picture. A defined corporate inspection may include the meeting room itself and other relevant areas or systems that could affect confidentiality.
You do not need to believe a surveillance device is already present. Tell us whether you want a one-off baseline assessment, an ongoing assurance programme, an upcoming sensitive-event inspection, a post-refurbishment or contractor-access review, or investigation of a specific concern. Only basic information is needed initially.
What a professional corporate inspection should include.
Technical inspection and room control before sensitive meetings.
Assess acoustic and RF paths beyond conventional bug detection.
For offices, boardrooms and commercial premises, we can scope a one-off baseline assessment or an ongoing technical-security programme combining scheduled reviews, sensitive-event TSCM and change-triggered inspections. Corporate TSCM starts from £995; small defined meeting-room inspections may start from £795. Broader assessments, routine assurance programmes and sensitive-event requirements are quoted according to scope and frequency.